Enterprise AI Security & Data Protection

Enterprise AI Security & Data Protection Platform

ThreatLens protects enterprise data across employees and AI applications by inspecting prompts and files, classifying data, and enforcing security policy before it reaches an AI model.

Adopt AI with confidence while maintaining security, privacy, compliance, and operational control.

ThreatLens AI Security controls AI access in real time. Need to prove what’s inside your AI systems and maintain audit-ready evidence? That’s ThreatLens AI Assurance →
Users & applications
Employees AI Applications
ThreatLens ThreatLens AI Security Control Plane Inspect · Classify · Enforce · Route · Audit
AI models & providers
ChatGPT Claude Gemini Azure OpenAI AWS Bedrock Enterprise Models

GenAI is already in your org.
ThreatLens makes it safe, and visible.

Employees paste source code, customer data, and contracts into public AI tools every day. ThreatLens gives them an approved way to work with AI, and gives security a single place to see, govern, and prove it.

What you achieve

Built for outcomes, not features.

From discovery to audit, everything you need to adopt AI safely across the enterprise.

01

Discover AI Usage

Identify sanctioned and unsanctioned AI usage across the organization.

02

Protect Sensitive Data

Inspect prompts and files for sensitive information before data leaves the organization.

03

Govern AI Access

Control which users can access which models and services.

04

Route Requests Intelligently

Direct requests to approved public or private AI models based on policy.

05

Audit Every Interaction

Maintain complete visibility into AI usage, prompts, and policy decisions.

Built for

One platform, every stakeholder.

AI governance is a shared mandate. ThreatLens gives each team what they need to move forward with confidence.

For CISO's

Reduce AI-related risk.

Quantify and shrink AI exposure across every team, tool, and model, with evidence to back it.

For CIO's

Enable secure AI adoption.

Give the business approved AI access without slowing innovation or adding friction.

For GRC Teams

Enforce governance and compliance.

Apply policy consistently and prove it with audit-ready evidence on every interaction.

For Security Teams

Protect sensitive information.

Stop sensitive data from leaving in prompts and files, in real time.

Inside the gateway

Four capabilities, one control plane.

Governance, data protection, real-time control, and compliance, applied to every AI interaction across your organization.

04Governance & Audit

Audit trails, session logging, and regulatory evidence, with data residency controls and compliance reporting.

03Runtime AI Control

Allow, redact, block, or route to an approved model, with granular model access control on every request.

ThreatLens
AI Security Platform

Always on

01AI Visibility

Full visibility into AI usage across the organization, with risk monitoring, policy management, and user behavior analytics.

02AI DLP

PII, source code, credentials, and financial data protection, with deep file inspection on every prompt and upload.

One control plane governs every AI interaction, without replacing the tools your teams already use.

How it works

One gateway between enterprise users and every model.

Every request, from a chat window, an IDE plugin, or an internal app, is intercepted, inspected, and decided in milliseconds before it ever reaches an AI provider.

Where AI is used
EmployeesChat · assistants · drafting
AI applicationsEmbedded AI features · API
FilesDocuments · spreadsheets · exports
AI Gateway layer

ThreatLens AI Security Platform

Inspects every prompt and file against your DLP engines and policies, then decides, in real time.

  • DLP inspection, PII, secrets & code
  • Policy decisioning & routing
  • Inline redaction & blocking
  • Private / local model routing
  • Immutable audit logging
Outcome

Governed AI access

Employees get the AI they need, while sensitive data is redacted, kept in a private model, or blocked, with a full audit trail.

Policy decides

Enterprise users work with AI freely. ThreatLens inspects every request. Your data stays governed.

Coverage

Secure every AI entry point.

One gateway in front of the consumer AI apps, enterprise applications, and private models your teams already use.

ChatGPTOpenAI
ClaudeAnthropic
GeminiGoogle
Azure OpenAIMicrosoft Azure
Enterprise AI ApplicationsVia API
Private AI ModelsSelf-hosted · in-tenant
Policy engine

Four ways to decide, on every request.

Build policies from conditions, data classes, groups, and providers. The gateway applies the right action automatically, in line.

Allow

Clean requests pass straight through to the approved model with full logging.

Logged & audited

Redact

Strip emails, phone numbers, secrets, and PII from the prompt before it's sent, automatically.

Sensitive values removed

Block

Stop database dumps, credentials, and restricted files at the edge. Nothing reaches the provider.

Stopped at the gateway

Route to approved model

Send confidential and regulated data to an approved private or local model that never leaves your tenant.

Stays in-house
For enterprise users

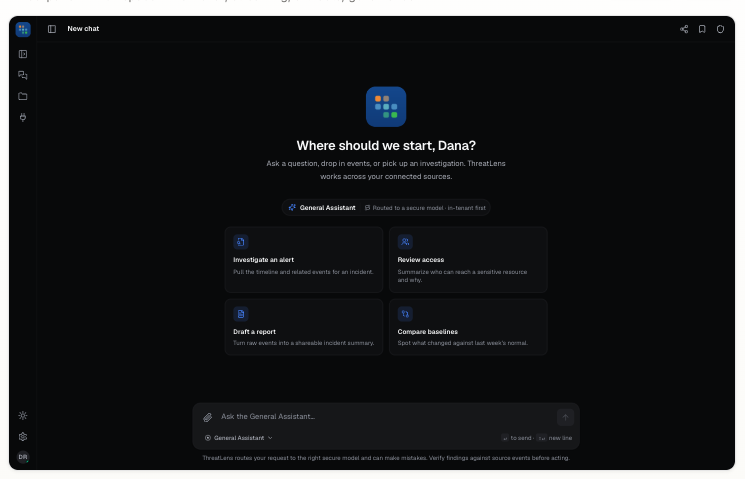
Secure AI access employees can actually use.

ThreatLens gives every employee an approved, policy-checked AI assistant for everyday work. They can draft, summarize, and analyze while the gateway checks prompts and files before anything reaches an AI provider.

  • Approved AI chat and assistants
  • Inline sensitive-data detection
  • Automatic model routing
  • Clear notices when content is redacted or blocked
app.thethreatlens.com/workspace
ThreatLens secure AI workspace
For security & data officers

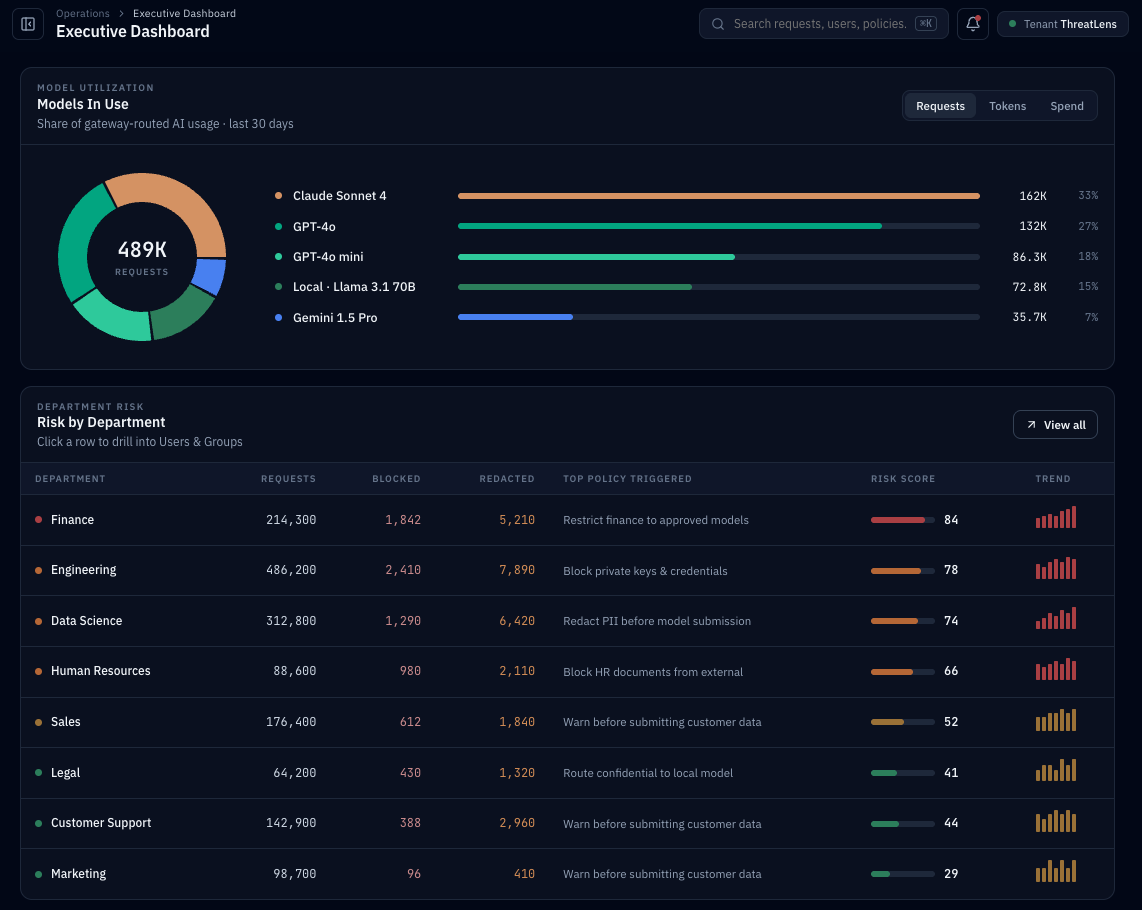
A security & governance console for every AI interaction.

See every prompt flowing through the gateway, what sensitive data was detected, and which policy decided it. Triage incidents, investigate activity, and export board-ready reports.

  • Executive dashboard & risk trends
  • Live activity monitor with full forensics
  • Incident triage & investigation
  • Multi-step policy builder
  • Immutable, audit-ready record
console.thethreatlens.com/dashboard
ThreatLens governance executive dashboard
Shadow AI detection & visibility

Surface shadow AI and know exactly what AI is doing with your data.

Understand how AI is used across your organization and identify unsanctioned, shadow AI usage before it creates compliance or security risk, with continuous AI usage monitoring and full risk visibility.

1.84M
AI requests governed every month
8,142
Risky requests blocked at the edge
23,907
Prompts redacted before sending
52,020
Sensitive-data detections surfaced

Illustrative figures from a representative deployment.

Works with your stack

Built to work with your DLP engines and approved providers.

ThreatLens connects to the DLP engines, identity systems, and AI providers your organization already runs.

DLP integration paths · available now

Connect your existing DLP as authoritative, advisory, or most-restrictive-wins policy inputs over standard ICAP or REST.

ICGeneric ICAPStandard ICAP path
REGeneric RESTREST connector

DLP Integration

Prebuilt connectors for the DLP engines your organization already runs.

MPMicrosoft Purview
SYSymantec / Broadcom
FPForcepoint DLP
NSNetskope
ZSZscaler
GCGoogle Cloud DLP

Approved AI providers

Route employee AI requests only to the model providers and deployment options your organization approves.

OpenAICustomer-approved
AnthropicCustomer-approved
Google GeminiCustomer-approved
LOLocal / vLLMPrivate deployment
+Your approved providersConfigurable connection

Available integrations depend on your deployment model. Bring your approved AI providers via configurable provider connections.

Built for trust

Enforced. Auditable. Provable.

Every decision the gateway makes is tied to a policy and written to an immutable record, so you can show regulators, auditors, and your board exactly how AI is used.

Immutable audit log No-train & retention controls Per-request forensics Data-residency routing SSO / SAML enforced

SOC 2 (In Process) · deploy in cloud, private cloud, or air-gapped.

Deployment

Runs where your data lives.

Deploy the gateway in your cloud, a private VPC, or fully air-gapped on-premises, with a local model option so confidential data never leaves your environment.

Explore our Trust Center →
SaaS Private Cloud On-Premises
The difference

Beyond prompt security.

Most AI security products stop at prompt filtering. ThreatLens combines data protection, governance, access control, intelligent routing, and auditability into a single AI Security Platform.

Most AI security tools
  • Prompt filtering
  • Sensitive data protection
  • AI governance & visibility
  • Model access control
  • Intelligent model routing
  • End-to-end auditability
ThreatLens AI Security Platform
  • Prompt & file inspection
  • Sensitive data protection (DLP)
  • AI governance & visibility
  • Model access control
  • Intelligent model routing
  • End-to-end auditability
Deployment

Deploy where your data needs to be.

Run ThreatLens in the model that matches your security, data-residency, and compliance requirements.

SaaS

Fast deployment.

Fully managed and continuously updated, live in days, not quarters.

Private Cloud

Dedicated environment.

Your own isolated tenant, in the cloud and region you choose.

On-Premises

Maximum control and compliance.

Runs entirely inside your network, data never leaves your environment.

The bigger picture

Part of the ThreatLens Ecosystem.

One company, one mission, investigation-grade truth and governed security across your stack and your AI.

FAQ

AI Security Platform, answered.

What security, governance, and compliance teams ask most before rolling out the gateway.

The ThreatLens AI Security Platform helps organizations securely adopt AI by protecting sensitive data, enforcing security policy, controlling AI access, and maintaining visibility across AI interactions.

As employees increasingly use AI tools, organizations need visibility, policy enforcement, and data protection controls to reduce risk and maintain compliance.

The ThreatLens AI Security Platform can control access to public and private AI models, including ChatGPT, Claude, Gemini, Azure OpenAI, AWS Bedrock, and organization-hosted models.

Yes. The platform inspects prompts and uploaded files to identify sensitive information and enforce organizational security policy.

At four enforcement points: a browser extension for ChatGPT, Claude, Gemini and other AI websites; a desktop agent for what enterprise users paste into the ChatGPT and Claude desktop apps; the AI gateway and API for enterprise apps, Microsoft 365 Copilot and approved models; and controls for AI agents and MCP servers. Every request follows the same inspection, classification and policy path, and the decision is enforced where the action happens.

Yes. ThreatLens applies policy to agent tool calls to MCP servers, per server and per tool, and allows or blocks each call before it runs. Every decision is recorded in the same tamper-evident audit trail as prompts and files.

The gateway analyzes prompts and uploaded files before they reach an AI provider. Policies can detect, block, redact, or route sensitive information based on organizational requirements.

Yes. Administrators can define policies that determine which users, groups, or applications can access specific AI models and services.

Yes. Organizations can route requests to approved private models, self-hosted models, or approved AI providers based on security and compliance requirements.

The platform maintains detailed audit logs of prompts, policy decisions, model usage, and user activity to support governance and compliance programs.

Yes. The platform provides centralized visibility, policy enforcement, auditability, and reporting capabilities to support enterprise AI governance initiatives.

The ThreatLens AI Security Platform is available as SaaS, private cloud, and on-premises deployments.

An AI governance platform gives organizations centralized control, visibility, and policy enforcement over how AI is used, spanning AI usage governance, data protection, access control, and audit so teams can adopt AI safely and stay compliant.

Shadow AI is the use of AI tools and models without IT or security approval, for example, employees pasting sensitive data into public chatbots. ThreatLens detects shadow AI usage and brings it under governance before it creates compliance or security risk.

With AI data loss prevention (AI DLP): ThreatLens inspects prompts and files for PII, payment data, source code, and secrets, then blocks, redacts, or routes them before information leaves the organization.

ThreatLens helps enterprises assess Microsoft 365 data exposure and governance readiness before expanding Microsoft Copilot, and maintains visibility and audit evidence across approved AI providers from a single control plane.

An enterprise AI control plane is the single layer between enterprise users and every AI model that inspects, governs, and routes requests, enforcing policy, applying AI guardrails, and giving you one place to see and prove how AI is used.

Get started

Give your teams AI, safely.

See how ThreatLens governs every AI request across your organization, from the employee workspace to the audit log — or take the free 5–7 minute assessment for a governance score and executive report.